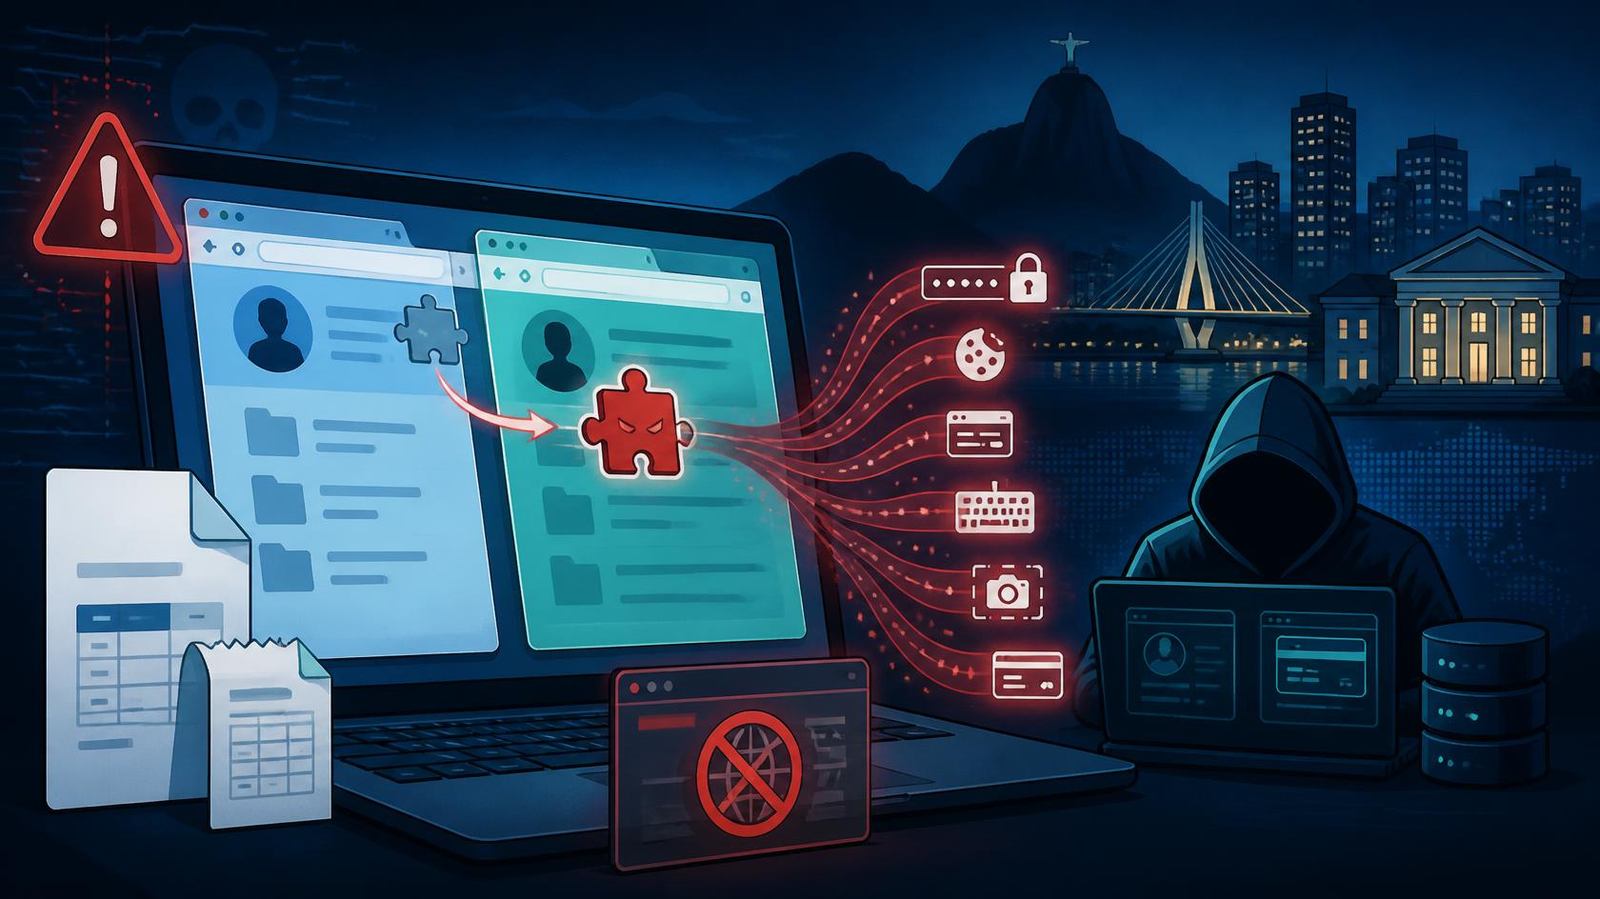
Elastic Security Labs reports that hackers are covertly force-installing malicious browser extensions in Chrome and Edge to steal passwords, cookies, and session data without user approval. The malware, linked to the KREMLIN bank toolkit, has launched at least seven campaigns targeting 12 Brazilian banks since May 2025.
The infection begins when users open disguised JavaScript files resembling bank receipts or invoices. The malware then copies extensions into browser profiles, modifies security files, and tricks browsers into loading them as trusted. These extensions, such as AVSync, can steal cookies, keylog inputs, capture screenshots, intercept traffic, and manipulate web pages. Researchers temporarily disrupted over 1,500 infections by blocking a related domain, mostly affecting Brazilian banking customers.
follow us on telegram for daily news


